Penetration testing · Moldova & Romania

We penetrate.
You choose where.

We stress-test the defenses of companies — banks, fintech, institutions — exactly the way a real attacker would. We show you where you’re exposed, with hard evidence and clear remediation steps.

We test forNIS2GDPRPCI DSSISO 27001
Recommended in writing by OTP Bank, Biroul de Credit and Paynet

Reports in Romanian, English or Russian · BNM and Law 48/2023 requirements

pentest.md/business
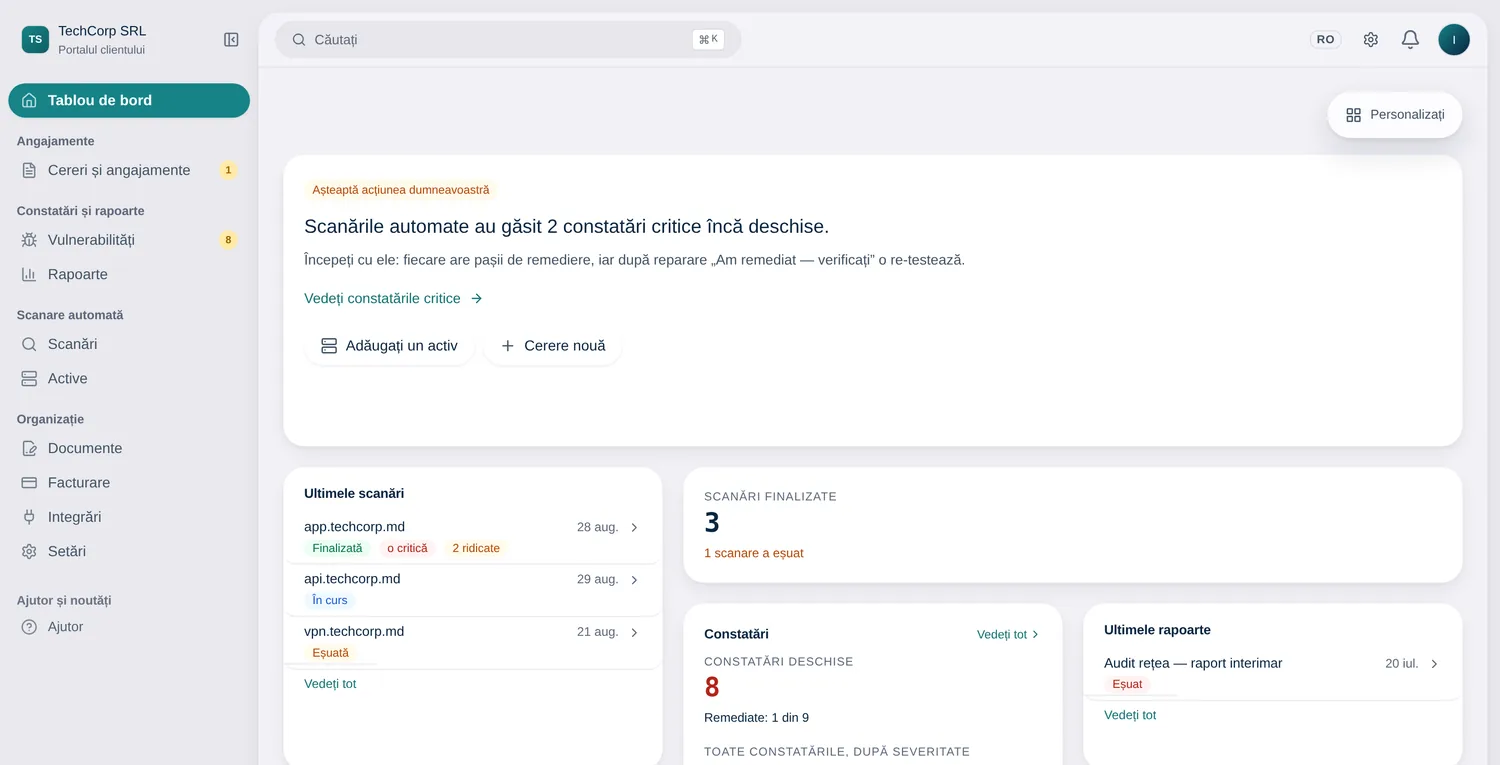
The Pentest.md security dashboard
500+ vulnerabilities
found and remediated
Organizations that entrusted us with their security
OTP Bank Qiwi Moldova Biroul de Credit Paynet Paymaster (RunPay)
The reality

A passed scan doesn’t mean you’re safe

Most breaches don’t happen because a firewall is missing — but because no one truly tested the defenses from an attacker’s perspective.

Attacks keep rising

The number of attacks on companies in the region grows year over year. Automation makes them cheaper, faster and more frequent — no organization is too small anymore.

Compliance is now mandatory

NIS2, GDPR and PCI-DSS require regular security testing. An incident with no evidence of due diligence means fines, audits and reputational damage.

The cost of a breach

A real breach means downtime, leaked data and lost trust — dozens of times more expensive than the proactive test that would have prevented it.

The impact of testing

From exposed to secured

Drag the handle and see what a full test changes — from critical vulnerabilities to a secured posture.

Before · Exposed
8.9
Risk score · Critical
  • ✕SQL Injection
  • ✕Weak passwords
  • ✕Exposed ports
  • ✕Outdated TLS
  • ✕Unencrypted data
After · Secured
1.2
Risk score · Low
  • ✓SQL Injection
  • ✓Weak passwords
  • ✓Exposed ports
  • ✓Outdated TLS
  • ✓Unencrypted data
What we test

We cover your entire digital perimeter

From internal infrastructure to public-facing apps — we test every point an attacker would target.

Infrastructure and network

Servers, internal and external networks, exposed services. We find the paths an attacker would use to get in and move laterally.

Web apps & APIs

OWASP Top 10, business logic, authentication and authorization. We test manually, beyond what a scanner catches.

Mobile apps

Android and iOS — insecure storage, communications, backend APIs and on-device data protection.

Cloud and configurations

AWS, Azure, GCP — misconfigurations, excessive permissions and exposures that lead to compromise.

Social engineering

The weakest point is often the human. We test how resistant your team is to real manipulation and pretexting.

Phishing simulations

Controlled campaigns that measure who clicks, who reports, and where training is needed.

Two ways of working

Scanning finds. The pentest confirms and goes deeper.

Use them separately or together: scanning keeps watch between two pentests, the pentest finds what no scanner sees.

Per project

Manual pentest

Engineers with personal certifications test like an attacker: authentication, access between roles, business logic, chains of vulnerabilities. Every finding is proven and comes with remediation steps.

  • Scope, schedule and signed authorization
  • Executive report and technical report
  • Retest after remediation
  • Engagement calendar (.ics) and a Slack or Teams channel
  • An attestation letter anyone can verify by its code

Quoted per project, based on the scope.

Request a quote →
Subscription

Continuous scanning

Automated, scheduled scans of your assets — applications, APIs, network, cloud. Findings are tracked in the portal until closed, with an owner, a due date and a retest.

  • Scheduled and on-demand scans
  • Findings without duplicates, with history and deadlines
  • JSON, CSV and SARIF export, Jira integration
  • Read-only public API and an MCP server for AI assistants
  • Remediation analytics (MTTR), compared with the platform median when there is enough data
  • Passive attack surface discovery, starting only from your company’s domains
  • Several companies under one account

Plans and prices are on the pricing page.

See the plans →
The platform

Your security, in one place

Order tests, track scans and receive reports — all from one clear panel, in real time.

pentest.md/business
Security dashboard List of service requests Compliance dashboard for Moldova’s cybersecurity law Remediation analytics: open findings, deadlines and age

The dashboard starts with what is waiting on you — here, two critical findings still open, with a direct path to them. Below: the scans, findings by severity and the latest reports.

How we work differently

We don’t just scan. We attack — under control.

Every engagement is a real attack simulation, not a list of automated alerts. Here’s what sets us apart.

Every finding manually validated

Certified engineers, not just scanners. We validate real impact, not just automated detection.

Attacker’s perspective

OWASP Top 10, realistic scenarios and controlled exploitation — we test the way someone actually would attack.

Actionable reports

CVSS severity, evidence, reproduction steps and clear remediation — for leadership and for the technical team.

Critical & regulated environments

Hands-on experience with banks, fintech and public institutions — and with NIS2, GDPR, PCI-DSS requirements.

15+
Projects completed
500+
Vulnerabilities found
10+
Happy clients
Compliance

Ready for regulatory requirements

Our reports are built to support audits and legal obligations — not just tick a box. We give you the evidence you need in front of regulators, partners and the board.

NIS2
EU security directive
GDPR
Data protection
PCI-DSS
Payment security
ISO 27001
Security management

Let’s talk about your security

A free, no-obligation consultation. We’ll tell you honestly where you stand and how we can help you sleep at night.